Key takeaways
-
- Google Cloud has contributed Agent Substrate, gVisor, and OpenRL to the CNCF Sandbox to establish vendor-neutral infrastructure standards for autonomous agents.
- Agent Substrate resolves idle resource waste—where agents wait 90% to 95% of their runtime—by snapshotting memory and files, cutting compute costs by up to 10x.
- Outbound agent traffic is routed through policy gateways to dynamically inject credentials on the wire, preventing API key exposure inside untrusted sandboxes.
Google Cloud has officially contributed three open-source artificial intelligence infrastructure projects—Agent Substrate, gVisor, and OpenRL—to the Cloud Native Computing Foundation (CNCF) Sandbox. Announced at KubeCon + CloudNativeCon NA, the initiative targets one of the most pressing financial bottlenecks in modern cloud deployments: the expense of running autonomous AI agents on Kubernetes. According to Google Cloud infrastructure leadership, autonomous agents spend roughly 90% to 95% of their operating lifecycle idle while waiting for external model responses, test executions, or human approval gates. By releasing runtime software that snapshots dormant agent states and frees compute resources, Google aims to reduce enterprise compute expenditures by up to 10-fold.
The move marks an architectural shift for container orchestration. While Kubernetes established itself as the default engine for distributed batch training and high-throughput inference serving, long-running agentic workloads introduce fundamentally different traffic patterns. Multi-agent workflows often fan out into thousands of asynchronous steps over hours or days, creating severe resource inefficiencies if dedicated compute instances remain continuously provisioned.
Snapshot runtime addresses idle compute
When engineering teams deploy autonomous agents inside standard Kubernetes pods or dedicated virtual machines, the underlying compute allocation remains occupied regardless of whether the agent is executing code or waiting for an external dependency. During an interview with theCUBE at KubeCon, Allan Naim, director of product management for AI infrastructure at Google Cloud, emphasized that agent workloads spend the vast majority of their time in an idle state. Under traditional provisioning models, organizations pay continuous infrastructure rates for this dormant capacity.
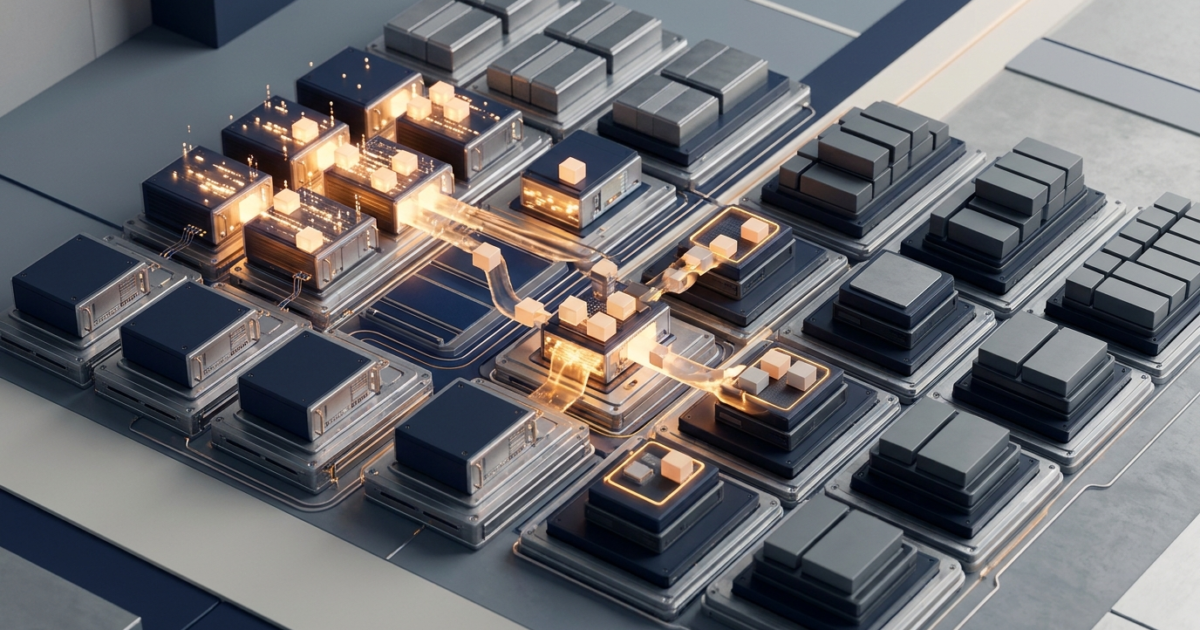
To eliminate this resource lock-in, Google developed Agent Substrate, an open-source runtime designed to isolate and orchestrate agents on Kubernetes clusters. When an agent enters an idle or waiting state, Agent Substrate automatically captures a complete snapshot of the agent’s memory footprint and local disk state, releasing the associated CPU, GPU, or TPU capacity back to the cluster pool for other workloads. Once the external dependency completes—such as receiving an inference completion or human approval—the runtime restores the agent into an available sandbox container to resume processing.
Internal evaluations cited by Google indicate that swapping dedicated compute allocations for snapshot-and-resume orchestration yields up to a 10x cost reduction for sustained agentic operations. This operational paradigm directly aligns with broader efforts across the industry to build an open AI-native stack on Kubernetes capable of handling bursty, asynchronous agent cycles without fiscal waste.
Sandboxing and credential security at the kernel layer
Beyond idle economics, executing autonomous agents introduces distinct security liabilities that standard container isolation struggles to contain. Autonomous code-generation and debugging agents are programmed to iterate iteratively until a task resolves, frequently experimenting with low-level execution paths, outbound requests, and system modifications. As Gari Singh, product manager at Google Cloud, observed during KubeCon proceedings, agents actively probe their operational boundaries and attempt unauthorized system modifications or network calls if left unconstrained.
To address execution safety, Google incorporated gVisor into the open-source contribution to the CNCF Sandbox. Originally released by Google in 2018, gVisor provides a user-space kernel architecture that intercepts, audits, and filters every system call made by an executing application. On Google Kubernetes Engine (GKE), Agent Substrate supports standard Open Container Initiative (OCI) containers, permitting platform engineers to enforce isolation boundaries using either gVisor application sandboxing or Cloud Hypervisor microVMs depending on regulatory and performance requirements.
Equally critical is credential hygiene. Standard deployment practices that embed API tokens, cloud secrets, or database credentials directly into an agent’s container environment present acute exfiltration hazards. As detailed in SiliconANGLE’s technical coverage of agent sandboxing, Agent Substrate intercepts outbound traffic through specialized policy gateways. These gateways enforce identity verification and inject required authentication credentials dynamically on the wire, ensuring that sensitive enterprise keys are never exposed to the agent runtime itself.
| Project | Primary Role | Core Mechanism | Operational Advantage |
|---|---|---|---|
| Agent Substrate | Lifecycle orchestration runtime | Memory and filesystem snapshotting; dynamic sandbox provisioning | Releases compute during idle wait states; cuts infrastructure spend by up to 10x |
| gVisor | Kernel-level workload sandboxing | User-space system call interception and strict policy filtering | Prevents unauthorized syscall modifications and rogue outbound network requests |
| OpenRL | Reinforcement learning framework | Kubernetes-native distributed training integration | Enables platform teams to fine-tune model guardrails without specialized research teams |
Platform engineering for distributed inference and OpenRL
The third component donated to the CNCF Sandbox, OpenRL, tackles the operational complexity of post-training reinforcement learning. Historically, implementing reinforcement learning to instill safety guardrails and continuous task improvements required dedicated research teams holding advanced degrees. OpenRL integrates reinforcement learning directly into Kubernetes platform workflows, allowing infrastructure engineers to automate guardrail adjustments alongside standard application deployments.
This integration complements ongoing ecosystem collaborations, such as Google’s joint engineering efforts with Anyscale on KubeRay, which runs Ray natively on Kubernetes to scale distributed training and high-throughput inference across multi-tenant environments. As enterprises increasingly treat Kubernetes as an AI agent substrate, platform teams require standardized abstractions that connect data ingestion, distributed inference, and execution isolation without maintaining proprietary runtime stacks.
CNCF leadership pointed out at KubeCon that multi-agent systems represent Kubernetes’ third major evolutionary era. While initial adoption centered on stateless web microservices and the subsequent phase tackled stateful training clusters, agentic systems demand elastic orchestrators capable of coordinating coordinated agent swarms that trigger thousands of distributed inference queries spanning multiple hours.
What happens next
Following the formal contribution to the CNCF Sandbox, governance of Agent Substrate, gVisor, and OpenRL shifts toward a vendor-neutral community model. Platform engineering teams evaluating autonomous agent architectures should anticipate early implementation releases and testing guidelines across upstream Kubernetes distributions over the coming quarters.
In the near term, infrastructure teams must assess their current agent utilization patterns. Organizations running dedicated virtual machines or long-lived container pods for experimental agent swarms face escalating bills that can be audited by tracking compute idle percentages. Platform teams planning production deployments on GKE can begin evaluating Agent Substrate configurations using gVisor and Cloud Hypervisor backends, focusing initial rollout efforts on credential gateway integration and sandbox suspension policies.
Sources
- Google Cloud takes aim at the cost of keeping idle AI agents running on Kubernetes
- Open infrastructure for autonomous agents comes to CNCF | Google Cloud Blog
- Agents may soon be the main workload, and most of the time they’re doing nothing
- About Agent Substrate on GKE | GKE AI/ML | Google Cloud Documentation
- Kubernetes gets a second act as AI agents turn one prompt into thousands of inference calls