Key takeaways
- Disparate local developer operating environments impose an expensive DIY maintenance tax, diverting engineering capacity from shipping product features to triaging base operating system updates.
- Standardizing on an enterprise Linux distribution stabilizes the software supply chain by providing backported vulnerability fixes while preserving Application Binary Interface (ABI) stability.
- Image mode for RHEL uses bootable container (bootc) architecture to define the operating system as code in Git, delivering dev-to-prod environment parity, atomic updates, and automatic rollbacks.
- The Red Hat Developer Subscription for Teams eliminates non-production licensing overhead, providing zero-cost RHEL deployments for developer workstations, CI/CD pipelines, and staging environments.
- Platform stability and shift-left automation directly improve core DORA benchmarks, shrinking Lead Time for Changes and reducing Change Failure Rates and Mean Time to Recovery.
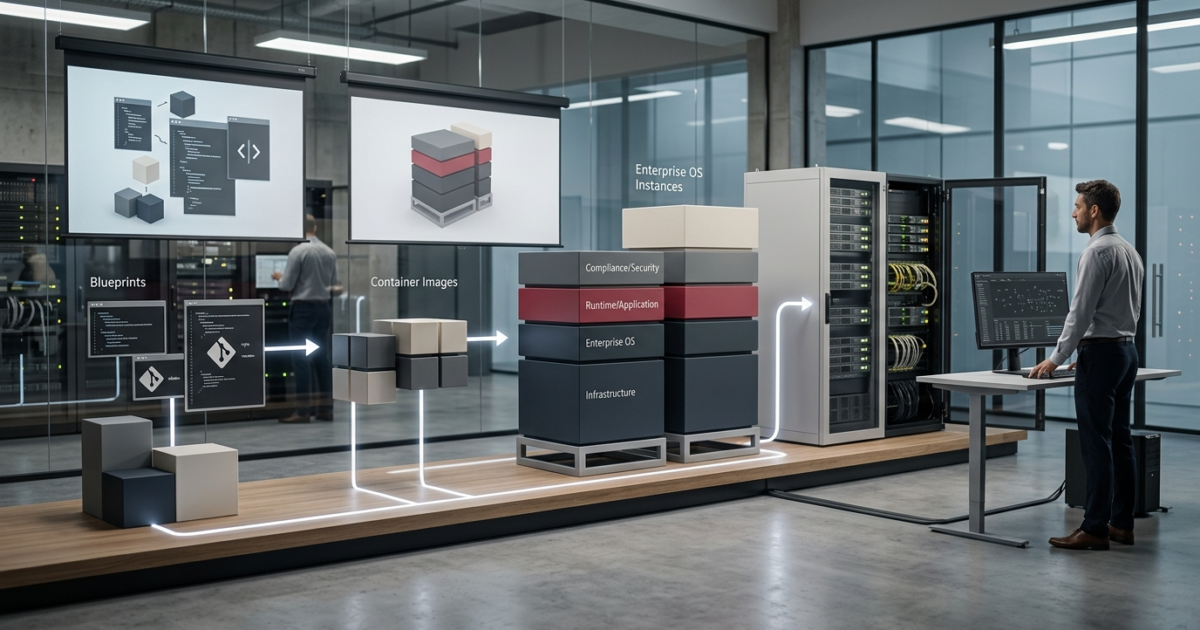
Enterprise engineering teams accumulate unsustainable developer technical debt when fragmented operating environments force engineers to triage broken local dependencies, reconcile configuration drift, and manually patch base distributions. Standardizing on an enterprise operating system such as Red Hat Enterprise Linux eliminates this maintenance tax by delivering continuous dev-to-prod parity, backported security remediation that preserves binary stability, and git-managed image mode deployments. By leveraging no-cost non-production access via the Red Hat Developer Subscription for Teams, engineering leadership can safeguard team autonomy while reducing operational churn and meeting corporate governance requirements.
The DIY maintenance tax in software engineering
Software engineering leaders frequently navigate a persistent structural tension: developers require tooling autonomy to innovate rapidly, whereas IT directors and security teams require predictable stability, centralized governance, and enforceable compliance controls. When engineering organizations grant unconstrained autonomy at the base operating system layer, teams inevitably fragment. Different squads adopt disparate community Linux distributions, varied kernel patch levels, and idiosyncratic automation scripts.
While community distributions provide an agile environment for initial local prototyping, managing them across distributed enterprise teams imposes an unintended “DIY maintenance tax.” Senior engineering capacity gets redirected into triaging upstream repository changes, compiling missing shared objects, and debugging broken local runtimes. When Common Vulnerabilities and Exposures (CVEs) appear, teams running unmanaged community distributions must pause planned sprint deliverables to research upstream tracker threads, create interim hotfixes, and test whether upstream patches break production services.
Industry findings documented in the 2024 DORA State of DevOps Report demonstrate that developer autonomy and platform stability are complementary drivers of engineering productivity and job satisfaction. Standardizing on enterprise Linux does not restrict developer choice; rather, it offloads undifferentiated infrastructure chores from application developers to an enterprise-grade vendor support tier.
| Operational Dimension | Community Linux Distribution | Enterprise Linux (RHEL) |
|---|---|---|
| Vulnerability Remediation | Manual upstream triage, custom compilation, and potential dependency breaks during zero-day mitigation | Tested, backported security patches preserving Application Binary Interface (ABI) stability |
| Environment Parity | Disparate local configs and bespoke build scripts leading to runtime drift | Immutable bootc container images checked into Git (OS as Code) with atomic rollbacks |
| Non-Production Licensing | Free community binaries, but requires internal engineering support and maintenance overhead | Zero-cost licensing across dev, CI/CD, and staging under the Developer Subscription for Teams |
| Compliance & Auditing | Manual configuration of CIS benchmarks and ad-hoc security policy enforcement | Pre-certified CIS Level 2 profiles, native SELinux mandatory access controls, and FIPS 140-2/3 validation |
Operating system as code with image mode and bootc
One of the primary historical drivers of developer friction has been the lack of parity between developer laptops, continuous integration (CI) runners, and live production clusters. The classic “it works on my machine” failure mode often stems from minor variations in system libraries, dynamic linkers, or systemd unit states. Enterprise Linux bridges this gap through image mode for RHEL, which manages the operating system as code.
Powered by open source bootable container technology (bootc), image mode enables platform engineers to define the entire host operating system within a single, version-controlled Containerfile. Developers build, inspect, and run these bootc images locally using Podman Desktop. The build pipeline then compiles the exact same container artifact into diverse target deployment formats, including cloud machine images (AMIs), virtual machine disk images (QCOW2 or VMDK), and bare-metal physical boot artifacts.
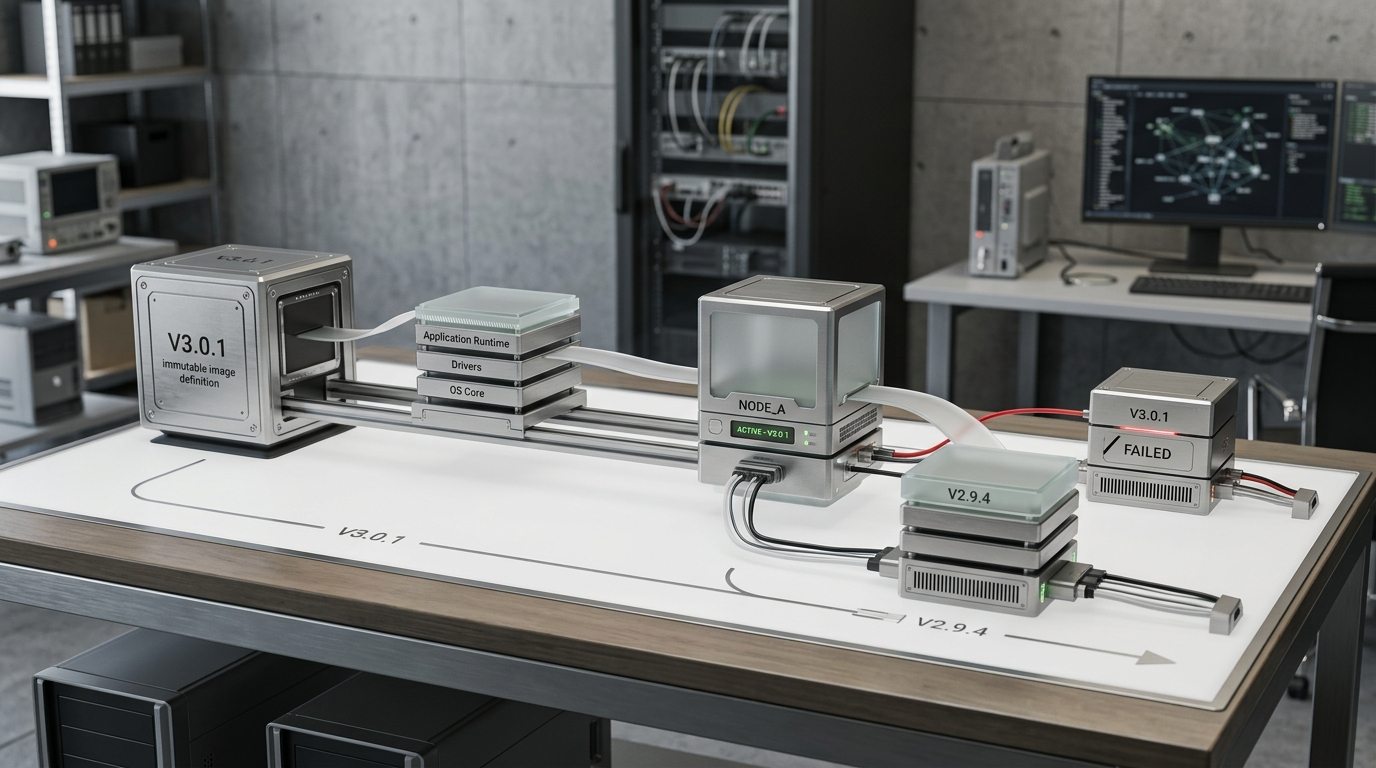
Because the underlying operating system executes as an immutable container image where system binaries are mounted read-only, runtime tampering and manual configuration drift are systematically prevented. All host updates originate as git commits that pass through CI/CD test gates. Crucially, host updates are applied atomically at reboot: if a system update encounters a boot failure or broken configuration, the node automatically rolls back to the prior known-good state, preventing extended downtime and emergency operational alerts.
Measuring platform stability against DORA benchmarks
Standardizing the underlying operating environment directly influences the four key DevOps Research and Assessment (DORA) delivery benchmarks:
- Lead Time for Changes: Pre-certified security baselines and pre-vetted dependencies allow release candidates to clear information security approval gates without weeks of manual remediation, moving code from merge to production faster.
- Deployment Frequency: Consistent container baselines and standardized base OS layers allow operations teams to schedule frequent automated deployments without initiating manual re-validation testing cycles.
- Change Failure Rate: Immutable OS images eliminate environment drift between staging clusters and production hosts, preventing unexpected runtime discrepancies caused by divergent package versions.
- Mean Time to Recovery (MTTR): When edge cases or service failures occur, image mode’s atomic rollback capability restores instances to a validated baseline state within minutes, keeping service restoration fast and predictable.
Licensing economics and supply chain governance
A frequent objection from procurement and finance teams regarding enterprise operating system standardization has been the projected cost of licensing non-production infrastructure. Engineering managers historically relied on community Linux derivatives because purchasing enterprise subscription seats for hundreds of local developer laptops, ephemeral CI test runners, and multi-tenant staging clusters was deemed cost-prohibitive.
The Red Hat Developer Subscription for Teams resolves this pricing barrier. Under this programmatic licensing tier, organizations pay strictly for production workloads and a narrow tier of internal mission-critical tools requiring commercial production service-level agreements (such as central issue trackers or private source repositories). Development workstations, ephemeral CI/CD pipelines, and pre-production staging clusters incur zero licensing costs, allowing platform teams to standardize developer environments without straining departmental operational budgets.
Concurrently, managing supply chain risk has become an essential engineering discipline. Developers pulling raw dependencies from public registries risk introducing unmitigated vulnerabilities or malicious dependencies. High-profile incidents demonstrate how untrusted dependencies compromise corporate cloud environments, a threat pattern mirrored in how supply chain attacks target enterprise cloud credentials through unvetted software repositories.
To secure software pipelines without throttling engineering velocity, enterprise platforms deliver pre-vetted packages and signed container runtimes. Through Red Hat Trusted Libraries, engineering teams gain access to verified open source libraries accompanied by provenance attestations and active vulnerability scanning. Furthermore, teams are not restricted to RHEL-based application containers; certified Red Hat Hardened Images allow developers to run alternative runtimes with commercial enterprise security encapsulation on top of RHEL and Red Hat OpenShift.
Local developer workspaces also require containment, particularly as engineers integrate generative AI models and local autonomous agents into their daily coding routines. Within Red Hat Desktop, the kaiden application provides dedicated sandboxing for testing agentic tools in reproducible, isolated runtime environments without granting broad access to host credentials. Complementing these local isolation controls, shift-left integration with Red Hat Lightspeed embeds predictive analytics and AI-assisted governance directly into RHEL pipelines, enabling developers to validate operating configurations and verify supply chain security baselines prior to cluster deployment.
Bottom line
Standardizing developer environments on an enterprise Linux foundation represents an architectural trade-off: organizations exchange the hidden operational friction of custom, self-maintained distributions for predictable, vendor-backed operating platform stability. By removing non-production licensing barriers, enabling Git-managed OS-as-Code via image mode, and providing pre-vetted supply chain libraries, enterprise Linux enables engineering teams to eliminate technical debt while improving delivery metrics across the development lifecycle.
Sources
- Developer-first innovation: Reducing technical debt with Red Hat Enterprise Linux
- Extend trust across the software supply chain with Red Hat trusted libraries
- Red Hat Developer Subscription for Teams
- Red Hat Launches New Developer Tools for Agentic AI
- Red Hat Lightspeed for Red Hat Enterprise Linux
- DORA | Accelerate State of DevOps Report 2024
- Shift left with Red Hat Lightspeed for Red Hat Enterprise Linux


