Key takeaways
- Shift to Runtime Control: Post-hoc observability cannot ensure compliance when autonomous agents delegate tasks across APIs; enterprises require deterministic, execution-time authorization.
- Shrinking Delegation Authority: Machine-to-machine task handoffs require authority to attenuate dynamically down the execution tree, preventing subordinate agents from inheriting broad privileges.
- Cryptographic Evidence Integrity: Audit trails demand cryptographically signed decision records paired with independent third-party verification to eliminate the trust vulnerability of self-reported logs.
- Sovereign Infrastructure Requirements: With 47% of enterprises managing hybrid or disconnected environments and 11% using air-gapped infrastructure, runtime governance must function without external SaaS dependencies.
AI agent governance is undergoing a fundamental architectural pivot from post-hoc observability to deterministic, runtime provable control. As autonomous software agents transition from isolated pilots into production environments, enterprise IT organizations face an acute authorization challenge: retrospective telemetry that merely reconstructs past actions is insufficient to demonstrate compliance, data integrity, or tenant isolation. Securing autonomous workflows requires cryptographic verification of agent authority before execution occurs, real-time contextual policy enforcement at the gateway layer, and immutable audit trails that link human delegators to downstream machine actions. Without verifiable proof of authorization at every delegation step, enterprises risk policy circumvention, credential hijacking, and catastrophic regulatory non-compliance.
For more than a decade, enterprise monitoring relied on observability: logging inputs, tracing distributed calls, and aggregating telemetry in centralized dashboards. If a microservice failed or a database query stalled, site reliability engineers parsed logs to identify the root cause. However, autonomous agents do not behave like static microservices. An agent tasked with resolving customer disputes or automating financial reconciliations might ingest natural-language instructions from a user, formulate an execution plan, delegate subtasks to secondary specialist agents, invoke external APIs, and alter production records. At every step in this chain, the scope of authority must dynamically shrink rather than expand, ensuring that an agent cannot exceed the mandate granted by its delegator.
Why Observability Fails the Agentic Access Model
Traditional enterprise access controls were architected around two stable assumptions: human operators operating through authenticated sessions and automated workloads executing deterministic scripts via static service accounts. Neither paradigm accommodates agentic workflows. When an autonomous system delegates tasks across microservices, authority propagates through machine-to-machine handoffs at high speed. A static API key or bearer token indicates that an agent possesses credentials to reach an endpoint, but it provides no guarantee that the specific operation is appropriate within the surrounding operational context.
According to an analysis on AI governance shifting toward provable control, relying solely on identity tokens creates a false sense of security. Sudeep Goswami, chief executive officer of Traefik Labs, points out that physical access control illustrates the limitation: an employee badge permits entry into a commercial office building, but that credential alone does not grant authority to approve an outbound corporate wire transfer or access personnel files. In the same way, an agent holding valid credentials must be evaluated dynamically: is this specific system allowed to execute this particular action right now, given the user prompt, target data classification, and active environmental constraints?
The scale of unmanaged agent creation compounds this architectural gap. Andreas Prins, who leads sovereignty strategy at SUSE Group, noted during a recent industry discussion that an executive discovered their engineering organization had deployed approximately 8,000 uncataloged agents across various internal environments. When IT leadership cannot enumerate active agents, establishing accountability or monitoring blast radiuses becomes impossible. This reality mirrors the software supply chain crisis, where untracked dependencies introduce unmonitored attack vectors.
Compounding the problem, autonomous agents that interface with web endpoints or third-party tools are vulnerable to manipulation. Security vulnerabilities such as BragJack attacks that hijack browser agents through rogue extensions demonstrate how quickly prompt injections and unauthorized extensions can divert an agent’s intended function. If enterprise governance relies only on post-hoc log parsing, malicious exfiltration or unintended configuration updates will be detected only after the damage has already occurred.
Mechanisms of Provable Authorization and Shrinking Authority
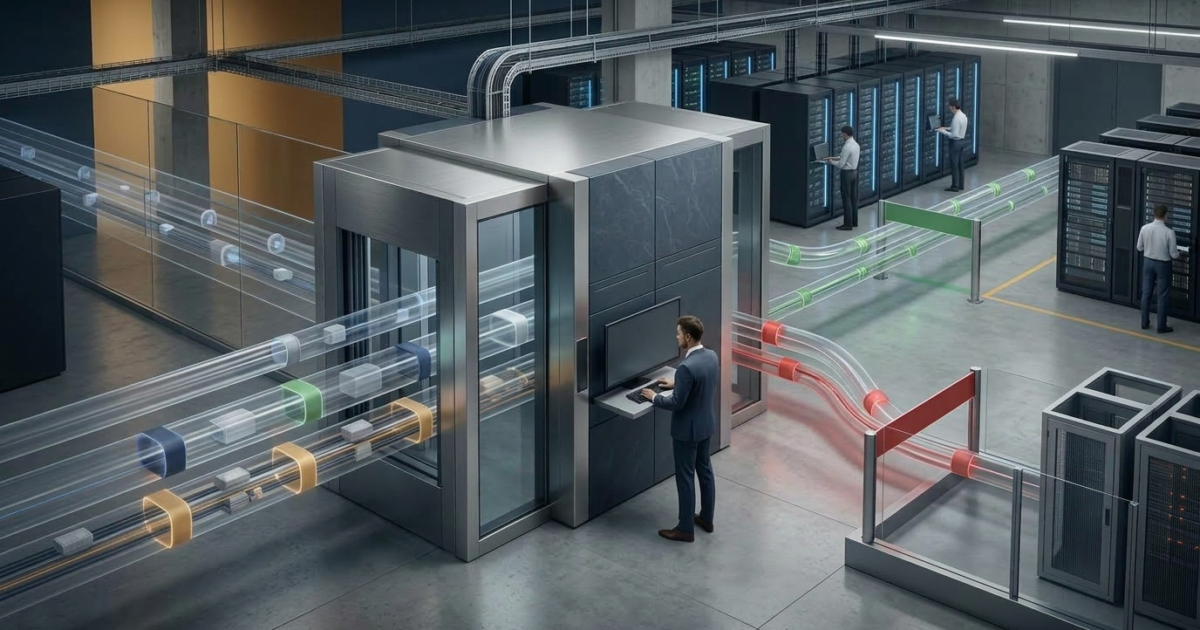
To prevent authority leakage across delegation chains, enterprise architectures must enforce runtime policy boundaries directly within the operational path. Rather than granting broad, standing permissions, governance systems must enforce deterministic authorization rules at the gateway where agents interact with enterprise APIs, databases, and microservices.
This runtime architecture relies on several interconnected mechanisms:
- Delegation Authority Shrinking: When a primary agent delegates a subtask to an auxiliary agent, the subordinate system must receive a strictly reduced subset of permissions. Authority must attenuate down the execution tree to prevent privilege escalation.
- Context-Aware Policy Evaluation: Policies must incorporate runtime variables, including user intent, session risk scores, data sensitivity, and operational parameters, evaluating each request against organizational rules before execution.
- Bilateral Action Recording: Enforcing gateways must record both permitted and denied actions. Documenting rejected requests is critical to proving that guardrails actively prevent policy violations and helps security teams identify misconfigured agent instructions.
- Contextual Action-Level Approvals: For sensitive operations such as bulk database exports, firewall rule alterations, or administrative privilege escalation, static credentials must be superseded by automated or human-in-the-loop review gates.
Research published by Hoop.dev on action-level approvals for AI governance emphasizes that static, broad credentials must be replaced with contextual review gates. By evaluating operations at the discrete action level rather than granting ambient session-wide trust, organizations establish verifiable boundaries that prevent runaway agent behavior.
Deterministic runtime systems maintain a linked context graph that binds the initiating user, the intermediate agent orchestrators, the active policy version, and the resulting API call into an auditable trace. As documented by LangGuard’s transparent runtime AI governance framework, provable authorization requires deterministic policy evaluation recorded at the exact millisecond an action executes, transforming passive monitoring into active boundary enforcement.
The Accountability Gap and Cryptographic Evidence
Shifting from retrospective monitoring to provable control addresses what enterprise researchers characterize as a widening accountability gap in autonomous systems. Traditional IT governance assumes a direct line of sight between human intention and system execution. When autonomous agents synthesize tasks independently, that relationship fractures.
In a technical assessment of the accountability gap in autonomous AI published by IBM, analysts stress that legacy identity frameworks designed for human operators fail to establish legal and operational liability when autonomous tools independently alter enterprise state. Without machine-specific identity and execution-time authorization, audits cannot definitively prove which model, agent version, or delegating human authorized a given mutation.
Furthermore, standard application logging suffers from an inherent trust vulnerability: the platform producing the log typically controls the storage and format of the record. Traefik Labs’ Goswami compares this dynamic to a vehicle odometer. If an automobile owner possesses the technical ability to reset or alter the mileage display, the odometer cannot serve as independent proof of vehicle wear. In enterprise IT, logs stored in mutable data lakes or managed by the same services executing agent requests remain susceptible to tampering, inadvertent omission, or silent revision.
To establish defensible trust, governance systems must produce tamper-evident, cryptographically signed records of every authorization event. These signatures bind the decision input, policy evaluation, and execution outcome. However, cryptographic signing alone is insufficient; enterprises also require independent, third-party verification mechanisms to validate that evidence records remain unmodified post-generation. This capability transforms raw observability streams into legally defensible audit artifacts.
| Dimension | Post-Hoc Observability | Runtime Provable Control |
|---|---|---|
| Evaluation Timing | Retrospective analysis after transaction completion | Deterministic evaluation in-line prior to execution |
| Identity Model | Static service accounts or shared human credentials | Discrete machine identity with contextual delegation scoping |
| Evidence Integrity | Standard text logs stored in mutable data warehouses | Cryptographically signed records with independent verification |
| Handling Policy Breaches | Alerts security operations after data has leaked or mutated | Terminates unauthorized actions at the gateway layer in real time |
| Delegation Management | Implicit trust inheritance across connected internal systems | Mandatory authority shrinkage across agent-to-agent handoffs |
Sovereignty, Compliance Burdens, and Air-Gapped Realities
The operational shift toward provable control intersects directly with enterprise data sovereignty. For organizations subject to stringent regulatory frameworks—such as banking, healthcare, critical national infrastructure, and defense—routing agent prompts, reasoning chains, and telemetry through third-party SaaS governance platforms introduces unacceptable legal and operational liabilities.
Data from ECI Research on AI agent governance reveals the magnitude of this friction: 48% of enterprise respondents identify navigating compliance documentation and collecting audit evidence as a major cognitive and administrative burden. Concurrently, 26% cite managing machine-to-machine secrets and API tokens as their single greatest hurdle when implementing zero-trust architectures for delegating agents.
Furthermore, field survey data indicates that 47% of enterprise IT organizations operate across hybrid environments combining connected and disconnected infrastructure, while 11% deploy generative AI models exclusively within on-premises or air-gapped data centers. In such environments, external cloud-hosted control planes cannot function. If an enterprise relies on an external SaaS dashboard to validate agent decisions, an infrastructure disconnection or sovereignty mandate breaks production workflows.
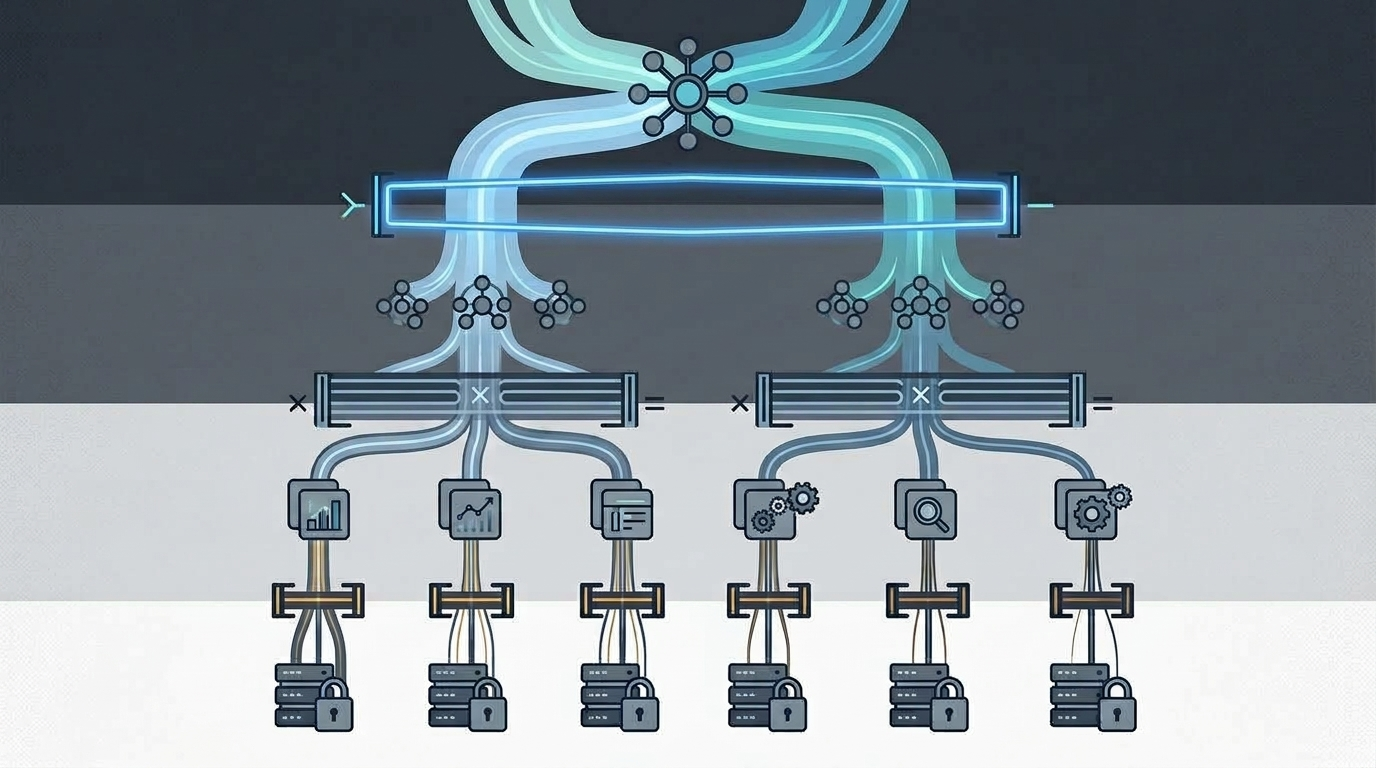
According to Traefik’s maturity model for AI sovereignty, achieving true operational independence requires architectural sovereignty across three distinct tiers: the model layer, the compute layer, and the gateway governance layer. Organizations must have the capability to deploy open-weight models on customer-managed compute clusters (such as SUSE-managed Kubernetes environments), govern interactions through localized API gateways, and generate cryptographic proof without outbound network dependencies.
In highly regulated sectors, identity and access management (IAM) serves as the indispensable control plane. As highlighted in research by Ping Identity on agentic AI in financial services, assigning discrete machine identities to every autonomous agent enables IT teams to enforce fine-grained entitlements, verify step-up authentication, and satisfy stringent regulatory audits without stalling organizational agility.
Evaluating Enterprise Agent Governance Readiness
Transitioning an enterprise from passive logging to provable runtime control requires systematic architectural alignment across security, platform engineering, and compliance teams. Technology leaders evaluating their infrastructure should assess four fundamental operational questions:
- Agent Discovery and Inventory: Does the organization possess automated tooling to detect, catalog, and monitor every active autonomous agent across development, testing, and production environments?
- Delegation Boundary Control: When an agent spawns a subagent or delegates an API call, does the system deterministically restrict authority, or does the secondary workload inherit broad administrative privileges?
- In-Line Gateway Interception: Can enterprise API gateways evaluate contextual security policies in-line to deny anomalous requests and log rejected attempts with identical fidelity to successful executions?
- Verifiable Evidence Provenance: Are audit trails stored with cryptographic proofs and verified against independent third-party mechanisms to guarantee records cannot be altered by administrators or compromised systems?
Bottom line
Observability tells engineering teams where an autonomous agent went and what data it touched after execution finished. In heavily regulated corporate environments, post-event discovery is no longer adequate. Scaling agentic AI safely requires provable runtime control: an architecture where machine identity is verified, contextual authority is systematically narrowed at every delegation step, and decisions are deterministically enforced at the gateway layer. Technology leaders who implement cryptographic verification, discrete machine identities, and sovereign runtime guardrails today will insulate their organizations against severe compliance failures while enabling autonomous workflows to expand with verifiable trust.
Sources
- AI governance shifts toward provable control – SiliconANGLE
- AI Agent Governance Is Moving to Provable Trust
- The accountability gap in autonomous AI | IBM
- Provable, Transparent AI Authorization and Audit Evidence | LangGuard – Deterministic Runtime AI Governance Platform
- Why Action-Level Approvals matter for AI governance AI model governance
- The Five Levels of AI Sovereignty: A Maturity Model for Infrastructure Control
- Why Identity Will Define the Future of Agentic AI in Financial Services | Ping Identity