Key takeaways
- Traditional IAM and IGA platforms govern design-time provisioning and perimeter single sign-on, leaving an “intent-to-execution gap” where autonomous agent tool invocation and internal data access remain unobserved.
- Deploying autonomous agents with standing permissions triggers OWASP LLM06 (Excessive Agency), escalating exposure when shared service accounts or persistent user credentials are used across workflows.
- Ephemeral delegation through RFC 8693 (OAuth 2.0 Token Exchange) ensures distinct audit attribution between users and autonomous actors using dedicated actor claims.
- Enterprise security frameworks such as NIST SP 800-53 Rev. 5 and NIST AI RMF 100-1 require behavioral, application-layer telemetry to detect valid-credential abuse (MITRE ATT&CK T1078) and enforce continuous authorization.
- Sustainable enterprise adoption relies on a balanced model: extending existing identity governance suites for human ownership, deploying micro-authorization policies at execution points, and integrating specialized observability for agent discovery.
Identity and access management (IAM) for AI agents is the enterprise security framework that governs autonomous software actors through attributable non-human identities, short-lived task authorization, and continuous runtime monitoring. While traditional IAM systems manage static user provisioning and perimeter single sign-on, autonomous agents dynamically chain tasks, invoke third-party tools, and access backend data stores with delegated privileges. Governed deployment requires closing the gap between policy intent configured in central identity providers and actual execution across distributed application stacks. Without continuous observability and strict delegation controls, enterprises expose critical infrastructure to excessive agency, credential leakage, and untracked lateral movement.
The Intent-to-Execution Gap in Agentic Systems
Enterprise identity architectures have long relied on a foundational assumption: access granted at design time matches the actions taken at runtime. Traditional Identity Governance and Administration (IGA) platforms, such as SailPoint and Saviynt, manage joiner-mover-leaver workflows, entitlement reviews, and role assignments. In human workflows, these design-time entitlements represent reliable boundaries because human operators follow relatively predictable operational sequences. When an employee logs in through single sign-on (SSO), perimeter authorization checks confirm group membership and issue a session token that remains valid for hours or days.
Autonomous AI agents invalidate this model. Unlike deterministic scripts or human workers, an agent operates with variable execution paths. Given an objective, a model reasons over available context, chooses tools dynamically, parameters are formulated on the fly, and sub-actions chain together without intermediate human intervention. Central identity providers (IdPs) record a successful authentication event at the application perimeter, yet they possess zero visibility into whether the agent subsequently executed a read query or initiated a mass data export. This divergence creates an operational intent-to-execution gap.
Compounding this disconnect is the accumulation of what security teams term “identity dark matter.” As development groups deploy internal agents, build prototypes, and integrate automated pipelines, agent credentials propagate outside central directory services. These non-human identities frequently manifest as hardcoded API keys, local service accounts, unrotated personal access tokens, or nested machine-to-machine integrations. Because they bypass corporate HR-driven onboarding pipelines, they escape regular entitlement certification cycles.
When an agent is provisioned with broad standing permissions, it directly encounters the primary threat vector formalized by the OWASP Gen AI Security Project as Excessive Agency (LLM06). Excessive agency occurs when an autonomous agent possesses functionality, network access, or system permissions beyond what its designated task requires. In the event of prompt injection, data poisoning, or model hallucinations, the agent can be manipulated into executing high-impact actions across downstream systems. Static configuration reviews cannot measure this exposure because the permissions themselves appear legitimate on paper; only runtime behavioral telemetry reveals the misuse.
This breakdown in operational visibility raises fundamental governance questions. When autonomous workflows cross internal boundaries and generate secondary impacts, organizations must clarify accountability and boundary enforcement, a challenge examined in our analysis of liability when autonomous AI agents escape operational sandboxes.
Core Architecture: Attributable Identity and Scoped Delegation
Establishing control over agentic systems begins with identity attribution. An autonomous agent must never operate under a borrowed human account or a generic, shared service credential. If an audit log records an executive’s service account updating a sensitive repository, security operations cannot determine whether that change originated from an authorized administrator or an automated agent executing an unexpected prompt path. Every agent requires an independent non-human identity tied to a designated human owner, an explicit operational purpose, and a finite lifecycle expiration.
To eliminate standing credentials and unmanaged secrets, the identity tier must prioritize workload identity federation and ephemeral credential exchange. The architectural standard for implementing delegated authority is RFC 8693: OAuth 2.0 Token Exchange. Rather than handing an end-user session token to an agent, the agent uses the token exchange mechanism to request an ephemeral, task-scoped access token from an authorization server.
RFC 8693 establishes explicit delegation and impersonation semantics through dedicated token claims:
- The Subject Claim (
sub): Identifies the principal on whose behalf the action is being performed, typically the human user. - The Actor Claim (
act): Explicitly identifies the acting entity, capturing the agent’s unique machine identifier. - The May Act Claim (
may_act): Defines constraints on which downstream automated actors are authorized to exercise delegated privileges.
As detailed in technical specifications from Ping Identity’s identity-for-AI standards, downscoped token exchange ensures that the issued credential carries strictly constrained scopes and brief validity windows tailored to a single task execution. If an agent task terminates after three minutes, the token expires automatically, neutralizing replay attacks and credential harvesting.
In distributed, multi-agent architectures, delegation complexities multiply. A primary orchestrator agent often delegates sub-tasks to specialized subagents, such as a code-generation agent calling a database-query agent. As highlighted by WorkOS in their architectural evaluation of multi-hop delegation, naive implementations pass single authorization tokens down the line, completely blinding the final resource server to the intermediate handoffs. Robust multi-hop governance requires cryptographically chaining actor tokens across each hop, enabling downstream APIs to validate that each intermediary was authorized to handle the request.
These identity constraints map directly to established regulatory controls. In federal and high-assurance commercial environments, the Access Control (AC) family within NIST SP 800-53 Rev. 5 applies directly to autonomous agents. Enforcing least privilege (AC-6) and separation of duties (AC-5) requires moving authorization decisions from coarse application boundaries directly to individual function invocations.
Runtime Observability and Continuous Authorization
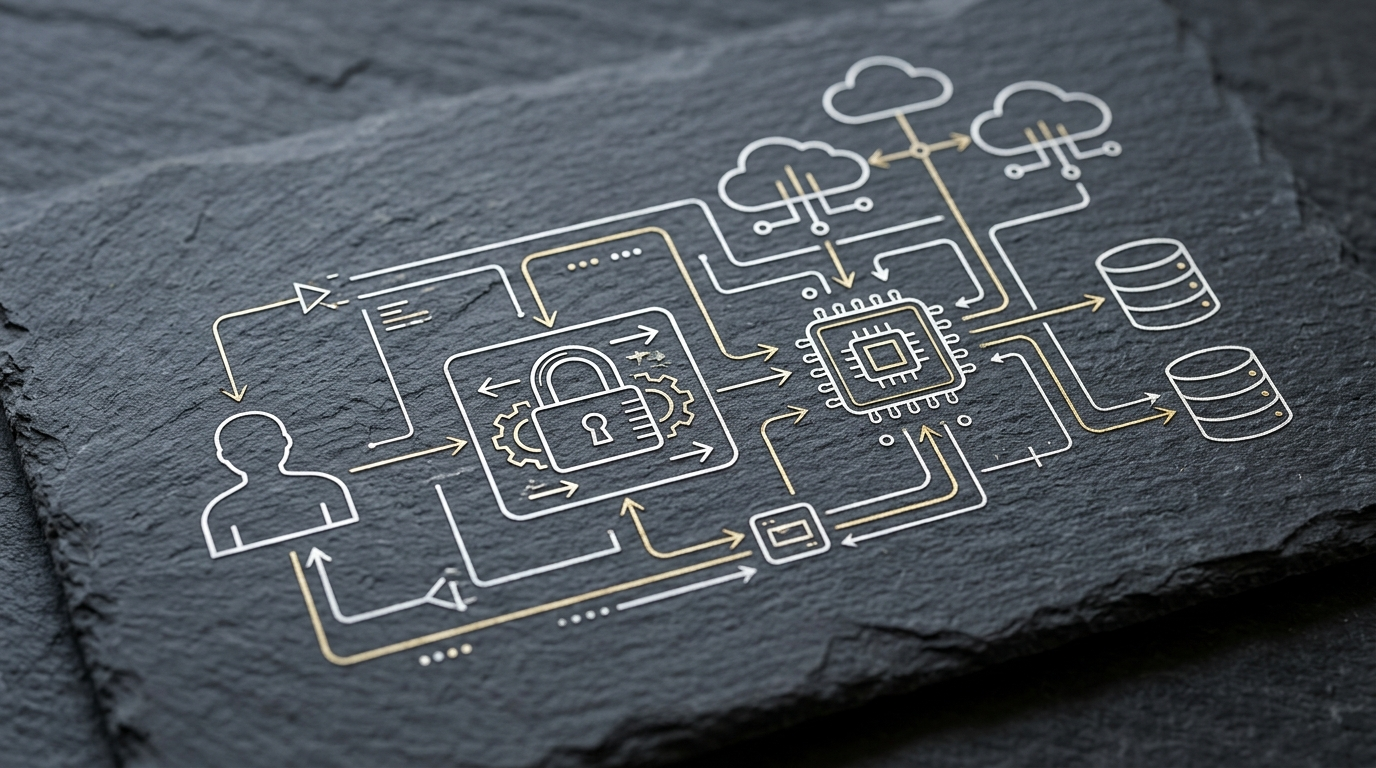
Authentication establishes identity, but runtime observability determines operational assurance. A conventional firewall or API gateway inspects credentials at ingress, admitting requests that carry valid cryptographic signatures. However, adversary tactics cataloged in MITRE ATT&CK under Valid Accounts (T1078) demonstrate that attackers routinely leverage legitimate credentials to execute malicious intent without triggering standard authentication alerts.
In AI-driven workloads, threat modeling must extend to specialized operational frameworks. The MITRE ATLAS (Adversarial Threat Landscape for Artificial-Intelligence Systems) matrix documents tactics specific to machine learning and agent ecosystems, including indirect prompt injection, data extraction, and tool hijacking. An agent compromise rarely looks like a brute-force intrusion; it appears as a series of syntactically valid API calls executed by an authorized machine identity.
Consequently, identity governance must incorporate continuous behavioral monitoring. Organizations cannot rely on periodic quarterly access reviews to detect unauthorized autonomous actions. Security telemetry must capture granular application-layer activity, including:
- Dynamic Tool Invocations: Logging which specific tools, scripts, or external APIs were called, along with runtime input parameters.
- Data Retrieval Boundaries: Tracking data stores accessed, tables queried, and the volume of records retrieved relative to the assigned task scope.
- Privilege Escalation Attempts: Detecting when an agent attempts to call management APIs, alter security groups, or generate secondary credentials.
- Execution Trace Lineage: Retaining complete reasoning paths and execution logs necessary to reconstruct the decision sequence that preceded an action.
This operational visibility aligns with the trustworthiness requirements defined in the NIST Artificial Intelligence Risk Management Framework (AI RMF 1.0). The NIST framework emphasizes that accountability and transparency depend on traceable system behaviors. Under NIST SP 800-53 Rev. 5 Audit and Accountability (AU) guidelines, audit trails must be granular enough to reconstruct the complete chain of events, establishing verifiable proof of behavior rather than theoretical compliance.
When runtime monitoring identifies a divergence between task intent and actual execution, the architecture must support continuous authorization. Unlike static binary access decisions, continuous authorization continuously evaluates risk posture, dynamically constrains tool access, and revokes active tokens the moment anomalous data queries or parameter manipulations appear. This shift reinforces why enterprise AI governance requires provable runtime control rather than passive dashboard observation.
Strategic Trade-offs: Extend, Build, or Buy
Enterprise technology leaders evaluating an IAM framework for AI agents face an architectural decision: should they extend their existing governance stack, build in-house policy middleware, or purchase specialized agent identity platforms? Each path involves distinct trade-offs across integration complexity, operational overhead, and detection efficacy.
| Strategy | Primary Control Layer | Integration & Staffing Requirements | Core Operational Strengths | Failure Modes & Limitations |
|---|---|---|---|---|
| Extend Existing IGA (SailPoint, Saviynt) |
Design-time lifecycle governance and entitlement certification | Moderate; utilizes existing identity engineering and compliance teams | Maintains unified compliance reporting, central audit logs, and established human ownership models | Blind to application-layer runtime actions, dynamic tool invocation, and ephemeral credentials |
| Build Custom Middleware (Internal Proxies & Sidecars) |
Runtime authorization, policy proxies, and API micro-segmentation | High; demands dedicated software engineering, cryptography, and ongoing maintenance | Custom tailored to proprietary agent frameworks; enforces strict task-level gating and RFC 8693 token exchange | Creates custom maintenance debt, fragments audit data, and risks policy desynchronization across teams |
| Buy Continuous Observability (Specialized Agent Security) |
Application discovery, credential mapping, and behavioral telemetry | Low to moderate; requires API connectors to cloud infrastructure and enterprise SaaS | Surfaces unmanaged identity dark matter; compares runtime execution against assigned task scope | Adds vendor cost; focuses primarily on detection and alerting rather than native identity provisioning |
For most enterprises, an effective architecture combines these approaches rather than relying on a single vendor:
- Extend the Core for Governance: Retain existing enterprise IGA platforms to manage identity registration, assign named human owners to each agent, enforce business justification workflows, and manage formal decommissioning schedules.
- Build Standardized Authorization Libraries: Provide development teams with centralized SDKs and API gateway sidecars that enforce RFC 8693 token exchange, short-lived credentials, and strict tool allowlists directly within the execution environment.
- Integrate Observability for Telemetry: Deploy specialized discovery and continuous monitoring tools that inspect application logs, surface shadow agent accounts across cloud tenants, and provide audit teams with telemetry-backed evidence of runtime compliance.
Bottom line
Deploying autonomous AI agents without a dedicated identity control plane introduces severe enterprise risk. Conventional IAM platforms were designed to manage human lifecycle states and perimeter access, leaving them ill-equipped to police autonomous agents that chain tasks, select tools dynamically, and access sensitive internal data. When organizations treat agents as generic service accounts with static API keys, they inadvertently construct an unmonitored shadow layer susceptible to prompt injection, valid-credential abuse, and excessive agency.
Achieving secure, scalable agentic operations requires establishing four non-negotiable architectural controls:
- Attributable Identity: Prohibit shared service credentials; ensure every agent identity traces to an accountable human owner with an enforced expiration policy.
- Cryptographic Delegation: Implement RFC 8693 token exchange to issue short-lived, downscoped task credentials that separate the human user from the automated actor.
- Runtime Enforcement: Enforce fine-grained tool allowlisting, strict data retrieval boundaries, and human approval gates for high-consequence actions.
- Telemetry-Backed Auditability: Capture granular application-layer logs that prove what the agent actually executed, aligning operations with NIST SP 800-53 Rev. 5 and NIST AI RMF 1.0 guidelines.
Organizations must transition through mature governance stages: moving from static inventory reviews to automated, event-driven lifecycle triggers, and ultimately to continuous runtime authorization. Policy intent without execution evidence is not security; operational assurance demands verifying that autonomous actors remain strictly within their authorized bounds.
Sources
- IAM for AI agents: A Practical Enterprise Framework
- LLM06:2025 Excessive Agency – OWASP Gen AI Security Project
- RFC 8693: OAuth 2.0 Token Exchange | RFC Editor
- Identifying agents with token exchange | Identity for AI
- AI agents and the multi-hop delegation problem — WorkOS
- Artificial Intelligence Risk Management Framework (AI RMF 1.0) | NIST
- MITRE ATLAS: AI security framework with 16 tactics and 84 techniques