Key takeaways
- managed threat hunting across artificial intelligence applications and autonomous agents via Falcon Guardian.
- The expansion introduces deep, telemetry-driven threat hunting across Google Cloud environments, establishing feature parity with AWS and Microsoft Azure.
- Consolidated under Falcon Adversary OverWatch Cross-Domain, the service eliminates domain-specific threat hunting SKUs across identity, cloud, endpoints, and SaaS layers.
- CrowdStrike data reveals that AI agents generated 2.5 times more detection leads than human operators, while eCrime cloud-conscious adversary activity increased 171% year-over-year.
- Managed detection and response (MDR) for AI workflows is supplemented by Falcon Complete for Falcon Guardian, which leverages CrowdStrike Agent Graph to trace attacks from prompt injection to endpoint execution.
CrowdStrike has expanded its Falcon Adversary OverWatch managed threat hunting service to cover generative AI applications, autonomous agents, and Google Cloud environments. Announced on October 30, 2026, the update introduces continuous 24/7 human-led threat hunting across AI workloads through CrowdStrike Falcon Guardian alongside telemetry-driven detection across Google Cloud infrastructure. The expansion consolidates multi-cloud and AI threat hunting under OverWatch Cross-Domain, eliminating the requirement for standalone hunting licenses across distinct operational environments. By combining runtime application context, raw cloud audit data, and identity signals, CrowdStrike aims to detect complex intrusions that jump between identity providers, AI assistants, and enterprise endpoints before automated tools flag standalone alerts.
Expanding managed threat hunting across AI and Google Cloud
Modern enterprise intrusions rarely remain confined to a single infrastructure boundary. As corporate environments integrate third-party software, identity providers, and multi-cloud hosts, adversaries pivot across operational silos to obscure their footprints. According to CrowdStrike’s announcement, Falcon Adversary OverWatch now analyzes more than 7 trillion events daily, uncovering over 14 million detection leads and delivering upwards of 36,000 verified threat notifications to organizations annually. The service draws on continuous tracking of more than 290 distinct adversary groups spanning eCrime syndicates, state-sponsored actors, and hacktivists.
The addition of Google Cloud brings the platform’s telemetry-driven hunting to feature parity with its existing coverage on Amazon Web Services (AWS) and Microsoft Azure. Rather than depending exclusively on pre-generated security alerts or vendor detection rules, OverWatch analysts inspect raw Google Cloud telemetry to identify anomalous operations early in the cyber kill chain. This focus aligns with CrowdStrike’s broader cloud hosting initiatives, including its expanded strategic partnership with Google Cloud to host the Falcon cybersecurity platform on Google Cloud infrastructure and satisfy enterprise data sovereignty mandates.
Cross-domain attacks and the rise of agentic threats
The incorporation of artificial intelligence into enterprise operations has created new operational exposures. Findings from the CrowdStrike 2026 Threat Hunting Report indicate that autonomous AI agents triggered 2.5 times more detection leads than human users over the measured period. This surge reflects the velocity and autonomy with which automated tools interact with enterprise files, software development environments, and internal networks.
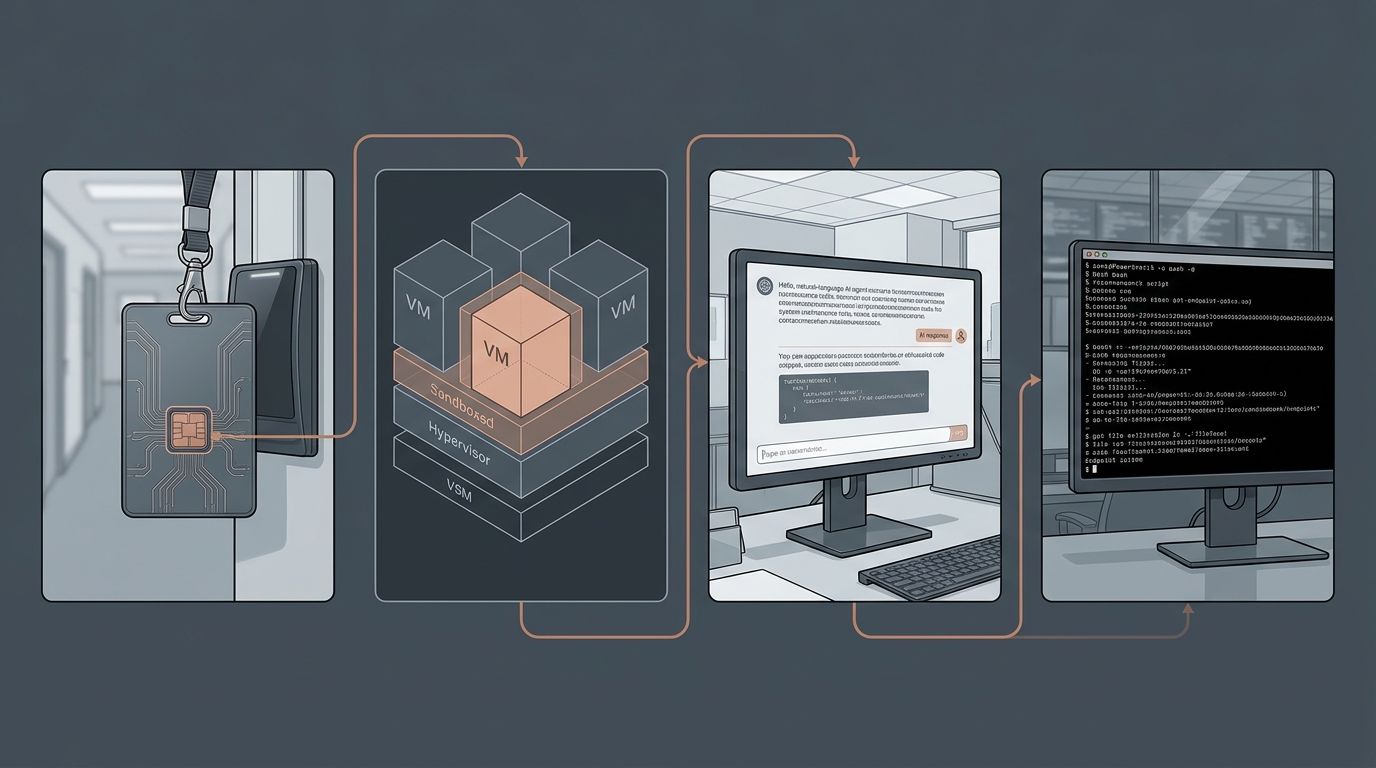
Adversaries increasingly leverage legitimate AI models and assistants to accelerate multi-stage intrusions. CrowdStrike highlighted a representative intrusion sequence demonstrating how autonomous tools can be manipulated during cross-domain compromises:
- Initial identity compromise: Threat actors harvest credentials through targeted phishing campaigns to establish unauthorized sessions with an enterprise identity provider.
- MFA circumvention and persistence: The adversary registers an unauthorized Quick Emulator (QEMU) virtual device within the organization’s multi-factor authentication (MFA) framework to maintain persistent access.
- Pivoting to SaaS and AI tools: Using the authenticated identity, the attacker accesses connected software-as-a-service (SaaS) environments and authorized large language model tools, such as Anthropic’s Claude.
- Agent-assisted enumeration: The attacker tasks the AI model with enumerating connected repositories, discovering internal databases, scanning agentic skill configurations, and drafting extraction scripts.
- Endpoint payload execution: The intrusion culminates in the deployment of a command-and-control (C2) backdoor on an enterprise endpoint, connecting internal systems back to attacker infrastructure.
When evaluated in isolation, single events—such as an unusual model prompt or an atypical script execution—frequently fail to trigger security thresholds. To counter this, Falcon Guardian operates as an AI Detection and Response (AIDR) mechanism embedded directly within the Falcon endpoint sensor, as detailed in reports on Falcon Guardian’s endpoint architecture. For response operations, CrowdStrike Falcon Complete for Falcon Guardian provides managed detection and response (MDR). Analysts utilize CrowdStrike Agent Graph to link prompts and tool requests with downstream system processes, tracing agent activity directly to endpoint execution.
Telemetry-driven cloud detection in multi-cloud environments
Cloud infrastructure continues to face persistent targeting from financially motivated threat actors. The CrowdStrike 2026 Threat Hunting Report recorded a 171% year-over-year increase in cloud-conscious eCrime operations. Attackers routinely weaponize valid credentials, exploit misconfigured storage permissions, and abuse native command-line interfaces to blend malicious operations into normal administrative baselines.
By hunting directly within raw Google Cloud audit logs, OverWatch analysts evaluate administrative behaviors that evade pattern-matching alerts. These behaviors include unauthorized role assignments, privilege escalation through service accounts, unusual cross-project data transfers, and unexpected compute instances.
| Environment | Telemetry Source | Targeted Adversary Behaviors |
|---|---|---|
| Google Cloud | Google Cloud audit logs, IAM events, compute telemetry | Service account abuse, unauthorized privilege escalation, cross-project lateral movement |
| AWS & Azure | AWS CloudTrail, Azure Activity logs, native infrastructure data | Stolen access key execution, resource hijacking, serverless compute manipulation |
| AI Applications & Agents | Falcon Guardian sensor telemetry, runtime model API interactions | Prompt injection, agent tool hijacking, unauthorized data harvesting, rogue agent discovery |
| Identity & Endpoint | Falcon sensor event logs, IdP session logs, Agent Graph | MFA bypass, credential dumping, rogue virtualization persistence, C2 establishment |
This integration reflects an industry-wide trend toward unified multi-cloud security telemetry, mirroring initiatives like Elastic’s security monitoring on Google Distributed Cloud. Consolidating these inputs into OverWatch Cross-Domain removes licensing fragmentation, allowing enterprise defense teams to maintain continuous monitoring without managing separate contracts for each cloud infrastructure vendor.
What happens next
The expansion of OverWatch to Google Cloud and AI systems signals an operational shift for security operations centers (SOCs) adapting to autonomous enterprise software. As organizations adopt productivity assistants and deploy tools like agentic AI assistants in enterprise cloud environments, security leaders must re-evaluate access permissions granted to automated agents.
In the near term, enterprise administrators should audit their multi-cloud telemetry pipelines to confirm that native Google Cloud audit logs are routed directly into centralized threat hunting platforms. Security teams should also catalog shadow AI usage and map the credential permissions provisioned to internal coding assistants and automated pipelines. As cross-domain attacks grow in speed and complexity, managed threat hunting services will increasingly depend on graph-based correlation to isolate compromised credentials before automated agents can be redirected against internal infrastructure.
Sources
- CrowdStrike Expands Falcon Adversary OverWatch Threat Hunting Across AI and Google Cloud
- CrowdStrike 2026 Threat Hunting Report | CrowdStrike
- CrowdStrike Falcon Guardian Defines the Next Generation of AI Security
- Stop Adversaries | CrowdStrike Falcon® Adversary OverWatch
- CrowdStrike and Google Announce the Falcon Platform on Google Cloud
- CrowdStrike launches Falcon Guardian for AI agents