Key takeaways
- pixels, specific paid UTM campaign mediums, time-of-day checks, and 3-to-5-day localStorage cooldowns—to remain dormant during security crawler visits.
- The detection pipeline pairs a frontline Graph Neural Network (GNN) analyzing JavaScript Abstract Syntax Trees (ASTs) with real-time Workers AI lightweight LLM verification and frontier model teacher ensembles.
- Malicious operations observed in the wild executed after-hours affiliate commission theft, clickless iframe attribution hijacking, search-hijacking backdoors with dynamic remote code execution, and the active suppression of nine analytics and support tools.
- Mitigating dynamic client-side threats requires continuous browser runtime visibility and behavioral telemetry rather than static point-in-time scanning or domain hash blocklists.
A modern e-commerce storefront can render products accurately, pass synthetic health checks, and complete customer transactions without error, all while unauthorized JavaScript silently executes within the customer’s browser. In a technical dissection of four malicious campaigns spanning eight payloads, Cloudflare revealed that its Client-Side Security machine learning systems detected active browser-level attacks across online retailers that traditional security scanners missed completely. Seven of the eight payloads were entirely absent from VirusTotal, while URLScan assigned no malicious verdict to any of them. By deploying selective execution gates, supply-chain tag injection, and runtime cloaking, modern client-side attacks evade static analysis, making continuous browser runtime monitoring and structural behavioral inspection critical for web infrastructure defense.
Why static scanners fail against dynamic client-side malware
Enterprise defense strategies have long relied on point-in-time vulnerability scanners, URL crawlers, and signature databases to inspect web assets. In client-side security, however, a single static snapshot of a Document Object Model (DOM) fails to capture how hostile scripts behave during authentic user interactions. Modern browser-targeted malware is engineered with selective execution routines: payloads remain completely dormant unless strict runtime conditions—such as device type, geographic origin, local time, specific HTTP referrers, and active user gestures—are satisfied.
The operational gap between traditional scanner indices and live execution was highlighted during Cloudflare’s analysis of the Lnkr malware family. While security researchers documented the broader Lnkr codebase years ago, a specific variant identified on an online retailer’s live storefront sat indexed within URLScan for nearly two and a half years with a “No classification” status, including during a direct automated scan in January 2024. Although VirusTotal eventually ingested and flagged the payload, historical telemetry failed to identify when that verdict was assigned. The script had been operating unhindered in production long before public feeds labeled its cryptographic hash.
When security teams rely strictly on file hashes and static reputation scores, detection arrives too late. An unknown or newly compiled JavaScript file generates a novel hash that evades static blocklists. Without inspecting dynamic execution flow and code structure, security tooling cannot distinguish between legitimate vendor libraries and malicious payloads disguised through standard minification, identifier renaming, and control flow flattening. Evaluating whether code is malicious requires moving beyond surface representation to evaluate semantic intent and runtime behavior, a shift explored in depth in TechNode HQ’s analysis of when to use SAST versus an LLM security scanner to secure modern software delivery.
Detection architecture: Graph Neural Networks and Workers AI LLMs
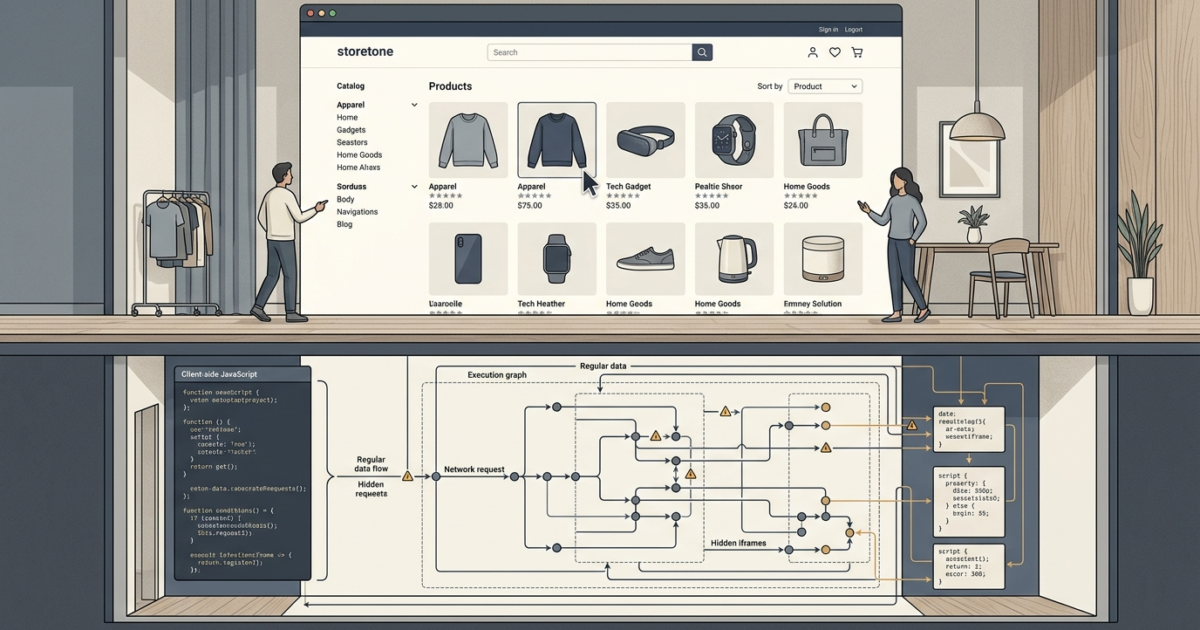
To detect evasive JavaScript in transit, Cloudflare implemented a multi-stage machine learning pipeline within its Page Shield and Client-Side Security systems. Rather than processing script files as linear strings of text, the frontline detection layer uses a Graph Neural Network (GNN). The GNN converts incoming JavaScript into an Abstract Syntax Tree (AST), modeling the code as a directed graph where nodes represent syntax elements and edges capture control and data flows.
By reasoning over syntax trees, the GNN maps which functions invoke external APIs, what sensitive variables are accessed, how data is packed, and where outbound network requests terminate. This topological approach allows the model to identify malicious execution patterns across minified, obfuscated, and dynamically assembled scripts without requiring known byte signatures or established domain reputations. The GNN operates with aggressive recall, filtering massive volumes of production web traffic down to the small fraction—under 0.3 percent—exhibiting anomalous structural patterns.
Scripts flagged by the GNN transition into an automated arbitration pipeline for secondary validation and classification:
- Workers AI Second Opinion: Flagged scripts are immediately evaluated by a lightweight Large Language Model (LLM) hosted on Cloudflare Workers AI. This stage acts as a real-time, low-latency filter that cross-examines the GNN’s structural findings against known benign programming idioms, filtering out false positives while maintaining alert fidelity.
- Frontier Model Teacher Cohort: For intricate, heavily obfuscated payloads where consensus is ambiguous, Cloudflare routes the script to an ensemble of automated judges termed “teachers.” This cohort incorporates frontier foundation models spanning six model families, including open-weight models executed on Workers AI. Each model acts as an independent agent inside an isolated sandbox session, utilizing a restricted JavaScript evaluation tool to unpack encoded string tables and inspect deobfuscated fragments.
- Weighted Decision Scoring: Teacher judgments are weighted based on each model’s standing in the Artificial Analysis Intelligence Index. The resulting composite score generates a calibrated probability distribution across four primary operational labels: benign, payment skimming (Magecart), other malware, and cryptomining.
- Human-in-the-Loop Feedback: Security analysts intervene only when a script is classified as malicious or when the automated teacher cohort fails to achieve a two-thirds majority consensus. These verified distributions are systematically fed back into GNN training runs, continually improving the model’s ability to classify novel evasion patterns.
Dissecting four in-the-wild storefront operations
Cloudflare’s machine learning architecture caught eight distinct payloads deployed across four hostile campaigns operating on legitimate retail and travel storefronts. These campaigns demonstrated diverse monetization models, ranging from affiliate commission diversion to administrative telemetry backdoors and marketing analytics blinding.
| Operation | Primary Objective | Delivery & Persistence Vector | Cloaking & Evasion Gates |
|---|---|---|---|
| After-Hours Affiliate Hijacker | Redirects product tap attribution to steal partner commissions | Multi-tag supply chain (GTM daisy-chaining) via typosquatted domain (adtargett[.]com); 3-to-5 day localStorage cooldown | Mobile viewport checks, weekend/time-of-day filters, MutationObserver late-DOM rendering hooks, console masking |
| Clickless Affiliate Theft | Generates unearned attribution requests on tourism booking sites | Invisible 1×1 off-screen iframe with no-referrer policy; automated hidden anchor tag programmatic click fallback | Public IP-lookup pre-flight network gate, deterministic Asia/Kolkata hourly time windows, 1-hour market throttle cookies |
| Repurposed Adware Backdoor (Lnkr) | Harvests session telemetry and provides arbitrary remote JavaScript execution | Direct storefront HTML injection via compromised credentials, modified templates, or compromised themes/plugins | Search keyword interception (‘virus’, ‘popup’) with persistent analyst opt-out in localStorage; modular inactive routines |
| Paid-Mobile Cloaker | Hijacks ad publisher revenue, replaces session recording, and blinds merchant observability | Stacked typosquat domain (sdk-amazonaws[.]com); secondary 600-day tracking cookie (_cart_dr) with zero-pixel beacon | Viewport < 477px, first-touch paid UTM mediums (ppc, cpc, sms), 325-entry IP string denylist, geographic exclusions, disables 9 monitoring tools |
The first operation, the after-hours affiliate hijacker, targeted mobile users browsing product catalogs on weekends. Using the browser’s MutationObserver API, the payload monitored the DOM for dynamically rendered product tiles that appeared after the initial page load. When a user tapped a product element, the script intercepted the click event, opened the intended merchandise page in a secondary tab to keep the customer engaged, and simultaneously routed the primary tab through an affiliate redirect link to plant an attribution cookie. To prevent detection by merchant staff, the script enforced a three-to-five-day cooldown stored in localStorage, remaining inactive on that browser during subsequent visits.
The second operation executed clickless affiliate fraud on a travel booking platform. The payload queried an external IP geolocation API—immediately terminating via an unhandled promise rejection (.catch(() => {})) if network requests were restricted, effectively thwarting sandboxes. The script ignored the returned location data, instead relying on hardcoded TradeDoubler configuration blocks mapped to Australian, American, and British markets. Evaluating local system time against the Asia/Kolkata timezone, the payload deterministically rotated affiliate requests during specific hours. Attribution was triggered by appending an invisible 1-pixel off-screen iframe configured with a no-referrer policy; if the iframe failed to complete within two seconds, the script generated a hidden anchor element and executed an automated programmatic click.
The third campaign repurposed the historical Lnkr browser-extension adware into an arbitrary remote code execution backdoor embedded directly into an e-commerce retailer’s HTML source. The script housed modular components, keeping legacy search-hijacking modules dormant while maintaining an active telemetry channel to remote command endpoints including scrprime[.]com and jullyambery[.]net. These endpoints allowed attackers to push secondary JavaScript payloads into shopper sessions at will. The code incorporated defensive evasions inherited from adware campaigns, inspecting Google search queries for keywords such as “virus” or “popup”; detecting two or more security terms caused the script to write a permanent opt-out flag to localStorage, silencing execution on security researchers’ workstations.
The fourth operation, a paid-mobile cloaker, focused on mobile visitors arriving from paid customer acquisition campaigns (tagged with utm_medium values including ppc, cpc, and sms). Upon validating that the viewport width was below 477 pixels and matching client IP prefixes against an embedded 325-entry denylist, the payload executed a targeted sabotage of store observability. It stripped script elements and neutralized inline references for nine monitoring platforms—including Lucky Orange, Segment, Optimizely, New Relic, Bugsnag, LogRocket, Hotjar, Microsoft Clarity, and the store’s Google Tag Manager container. It suppressed customer support widgets via CSS injection, purged Google Ads publisher slots to replace them with attacker-owned IDs, and deployed a rogue Microsoft Clarity recording ID, diverting telemetry while the storefront continued processing sales.
Supply-chain delivery paths and runtime cloaking mechanics
A critical finding from Cloudflare’s telemetry is how attackers exploit the marketing technology supply chain to deliver hostile payloads. In the after-hours affiliate operation, delivery was confirmed through a daisy-chain of tag managers: a primary Google Tag Manager (GTM) container loaded a secondary tag manager, which then injected the malicious script into the DOM. This multi-hop loading vector circumvents perimeter code reviews, as marketing and analytics teams frequently modify container configurations without DevSecOps approval.
Attackers also paired supply-chain distribution with sophisticated typosquatting to bypass domain audits. In the affiliate hijacking campaign, payload assets were hosted on adtargett[.]com, an imitation domain registered in 2025 designed to mimic adtarget[.]com (a digital advertising property established in 1998). The malicious site featured a fabricated agency landing page claiming to provide performance marketing services. In the paid-mobile cloaking operation, attackers deployed sdk-amazonaws[.]com, combining an imitation of Amazon Web Services with a subdomain referencing a prominent e-commerce marketing vendor. This layered impersonation disguised script origins within standard browser network inspector logs.
Beyond network camouflage, attackers deployed anti-analysis tactics within script execution paths. In the paid-mobile campaign, the payload evaluated a conditional check structured as Math.random() <= 1. While appearing to be a probabilistic execution throttle to an analyst reviewing obfuscated code, the statement is mathematically deterministic, always evaluating to true. In parallel, an alternate non-campaign branch contained logic requiring the session page counter to be simultaneously greater than negative one and less than negative two—a physical impossibility that ensured the branch remained permanently unreachable. Such techniques illustrate why security through obscurity has collapsed in modern enterprise systems: algorithmic graph analysis and AST modeling deconstruct these logical facades instantly.
Bottom line
The discovery of these eight stealth payloads confirms that client-side storefront security cannot rely on traditional perimeter firewalls, external URL scanners, or static hash databases. When attackers can gate execution behind screen widths, time zones, paid campaign tags, and multi-day browser cooldowns, a scanner querying a URL from a cloud data center will repeatedly encounter benign code.
Platform engineers, cloud architects, and security leaders responsible for e-commerce infrastructure must re-evaluate their client-side defense posture across three operational dimensions:
- Continuous Browser-Level Telemetry: Shift from point-in-time synthetic crawling to continuous monitoring of scripts executing inside authentic end-user browser sessions. Observability must track script additions, runtime DOM mutations, outbound network destinations, and cookie manipulation in live traffic.
- Tag Manager and Supply-Chain Governance: Restrict the autonomy of third-party script injection pipelines. Implement strict Content Security Policy (CSP) directives with cryptographic nonces, enforce Subresource Integrity (SRI) for external dependencies, and prohibit tag management containers from loading arbitrary nested scripts without code review gates.
- Behavioral and Structural Code Analysis: Deploy client-side inspection architectures capable of analyzing code intent and syntax graph topology. Obfuscation, dynamic string assembly, and domain rotation render signature matching ineffective; defense platforms must reason over JavaScript Abstract Syntax Trees to identify exfiltration, click hijacking, and observability suppression as they occur.